

ASOS is investigating a cyber incident after customers received an unauthorized app notification claiming hackers had accessed its Snowflake data environment. The retailer confirmed suspicious activity involving third-party communication platforms, but the claim that its Snowflake instance was compromised remains unverified.
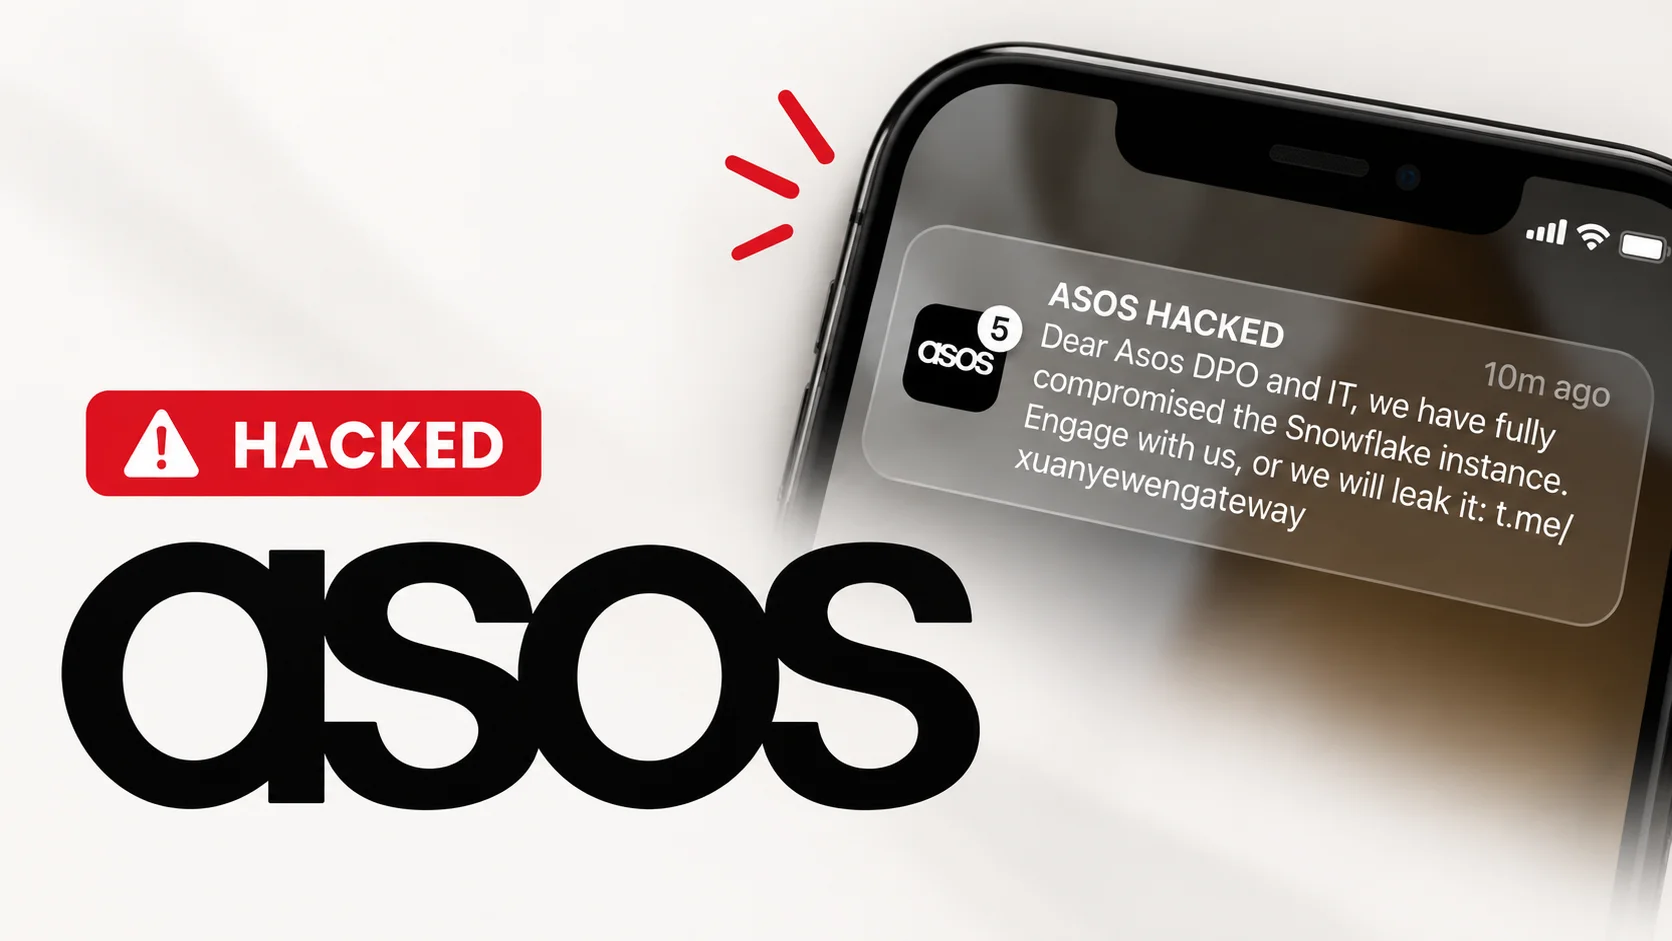
The notification appeared at around 10 am on October 6, 2026, under the heading “ASOS HACKED.” It addressed the company’s data protection officer and IT team directly, using a customer communication channel to deliver a public threat.

“Dear Asos DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it,” the message said. It included a Telegram link. The screenshot establishes what customers saw, but does not prove the claimed database compromise.
ASOS Confirms Unauthorized Activity
“We are investigating unauthorised activity involving third-party platforms that we use to communicate with customers,” ASOS said. The retailer confirmed an “unauthorised customer notification” and said it immediately restricted access to the notification platforms.
The company is working with specialists and relevant authorities. It said basic personal information, including names and contact details, may have been accessed.
“We do not believe that payment-card information or account passwords, were impacted,” ASOS added. This remains an initial assessment rather than a final account of the incident.
ASOS said its website and app were operating normally. It confirmed cyber security and business continuity insurance with a large global provider, while saying it was too early to measure any potential effect on trading.
Snowflake is a cloud data platform that businesses use to store and analyze information. Unauthorized access to a notification platform does not automatically demonstrate access to cloud databases, payment systems or the wider retail network.
Check Point’s Charlotte Wilson told the BBC that the attackers might be trying to embarrass ASOS through a public message. She stressed that the claimed Snowflake access had not been verified.
The notification appears designed to force contact by placing pressure on ASOS in front of customers. Investigators need to establish the entry point, the systems involved, and whether any customer records were copied.
Cybersecurity News previously reported on August 25, 2026, that ASOS customer accounts were accessed using compromised login credentials obtained outside the company. That incident was detected on July 28 and confirmed the following day.
The earlier case pointed to credential stuffing, where attackers try leaked username and password combinations against other services. Potentially accessed information included names, addresses, telephone numbers, dates of birth, and limited payment card details, such as the last four digits and expiration dates.
ASOS blocked affected accounts and required password resets on July 29. It also reported suspicious transactions that were blocked or canceled. No confirmed link connects that account access incident with the latest notification platform investigation.
ASOS shares fell more than 11%, with reports recording an intraday decline of up to 13%. The notification made the incident visible before its full scope was clear.
Customers should avoid the Telegram link, follow official ASOS updates, and watch for suspicious account activity. Unexpected emails or texts may exploit the incident to request passwords or payments. Anyone reusing an ASOS password elsewhere should replace those passwords with unique ones. Receiving the notification alone does not establish that a customer’s phone was hacked.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup into your SOC
