

Iranian state-aligned hackers have used a fake Dubai Airports recruitment process to target Iraqi critical infrastructure with a booby-trapped coding test.
The campaign, called Blinder Tunnel, turned a routine developer task into a quiet, potentially long-term route for remote access, persistence and network tunneling across a victim environment.
The operation was prepared as early as November 2025 and activated in March 2026 against a likely Iraqi software engineer.
Victims first received a convincing offline careers portal, then a personalized Visual Studio project framed as an at-home assessment for a development job. Unit 42 researchers identified the activity as CL-STA-1178 and assessed with high confidence that it aligns with an Iranian-nexus threat.
The group impersonated Dubai Airports IT staff, although researchers said they found no evidence of a compromise, breach or vulnerability in Dubai Airports systems.
The case shows why developer environments are becoming valuable targets. A project can look harmless to someone expecting a coding test, while trusted build tools execute attacker-supplied instructions before the victim has written or compiled a line of code.

Palo Alto Networks said in a report shared with Cyber Security News (CSN) that the campaign used cloud services to disguise its traffic.
Iranian Hackers Use Fake Dubai Airports Coding Test
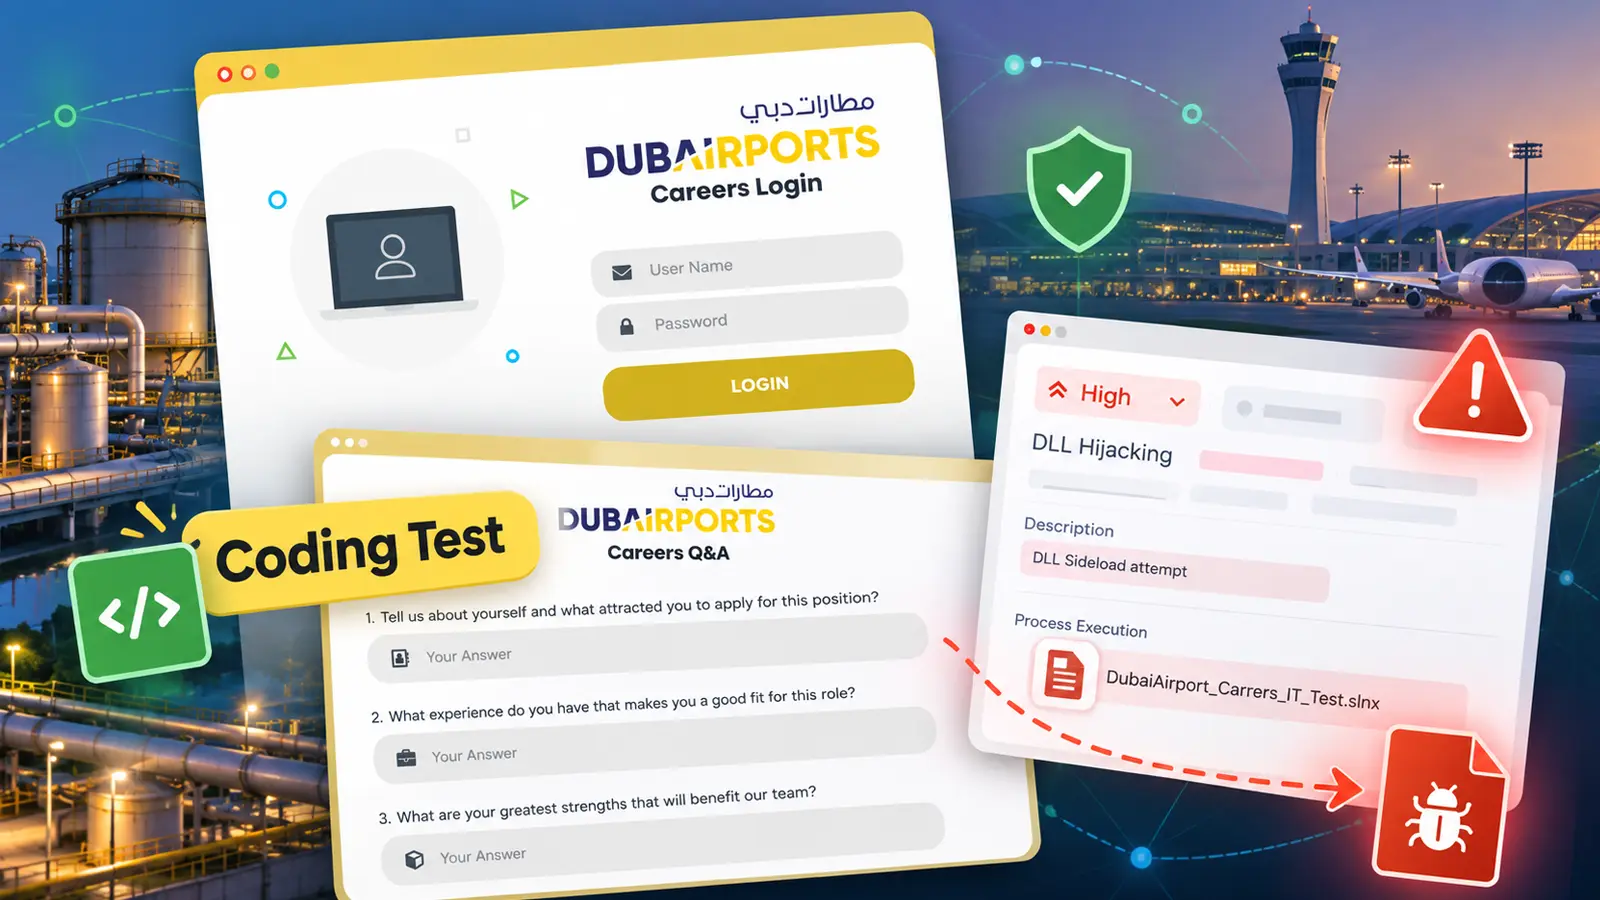
Beginning in late March, the attackers presented an Inno Setup application called Dubai Airport Careers as the first recruitment step.
It hosted a local imitation careers site, required credentials supplied by the supposed recruiters and displayed a 10-question HR form. The portal itself did not steal data or run malware, a deliberate choice meant to build trust before the next stage.
The follow-up archive, DubaiAirport_Carrers_IT_Test.zip, contained a Readme.md with instructions addressed to the target. It asked the candidate to open a C# Flight Management System project and correct a simple loop error.
That tailored lure reflects the same pattern of Iranian fake recruitment operations that use job opportunities to collect information or gain access.
Opening the project was enough to start the attack. A weaponized FlightManager.csproj abused Visual Studio’s normal background evaluation process, creating a deceptive RuntimeBrokers folder under local application data and launching RuntimeBroker.exe before the developer built the project.

Next, the attackers modified RuntimeBroker.exe.config to hijack AppDomainManager, forcing their code to run before the legitimate host application.
The configuration disabled Event Tracing for Windows, reducing the telemetry defenders use to spot suspicious .NET activity. Similar AppDomainManager hijacking tactics have recently appeared in other Iran-linked intrusion sets.
The final initial-access step used DLL sideloading. A renamed, legitimate Visual Studio hosting process loaded RuntimeBroker.dll, the ShelbyLoader V2 loader.
Security teams should investigate signed binaries that load unfamiliar DLLs outside normal system directories, and alert on unusual msbuild.exe activity, unexpected developer projects and changes to .NET configuration files.
GitHub C2 and Tunneling Tool
ShelbyLoader V2 created persistence through a registry Run value, profiled the host and contacted attacker infrastructure through GitHub’s API.
It uploaded a machine fingerprint, retrieved tasking and could fall back to encrypted data hidden in GitHub issue comments if the primary route stopped working. GitHub removed the infrastructure identified in the investigation.
The loader decrypted the ShelbyC2 V2 backdoor and used PsProxy.dll to run commands through the PowerShell engine without starting PowerShell.exe.
It also staged Blackwood, a memory-resident wrapper for Chisel that could establish encrypted tunnels and a reverse SOCKS proxy, allowing operators to move deeper into a compromised network.

This approach resembles how Chisel supports covert tunnels in other intrusion campaigns. The researchers linked the cluster to Iran through infrastructure, targeting patterns and an operational mistake in an audio file’s metadata, which referenced MusicDel[.]ir.
They also found related credential-harvesting infrastructure aimed at an Israeli entity in May and June 2026. Defenders should verify job-related files through independent contact channels, isolate suspicious systems, reset exposed credentials and review GitHub API activity that does not match normal development work.
Organizations should also use phishing-resistant multi-factor authentication and verify destination URLs before entering credentials.
Indicators of compromise (IoCs):-
| Type | Indicator | Description |
|---|---|---|
| SHA256 | 6e7d9b33f1e72ea1ede71373a604ecdb060dab7d42055179c1eede9ecd1fd239 | DubaiAirport_Carrers_IT_Test.zip, initial malicious archive |
| SHA256 | f5b12772db6817f7a765a6fe7565fd3d4f87edc28e42fe3ec0244a372a410fc9 | FlightManager.csproj, weaponized Visual Studio project file |
| SHA256 | 53f35e49eb9b271fd8cbcd3daacb525328dbf159a03dbd1c7adebe0363daa402 | RuntimeBroker.dll, primary RAT loader |
| SHA256 | 3fd810a3aa0039993393741b32287c367a9a5037a41e826906440887cdd3ed13 | PsProxy.dll, in-memory PowerShell execution engine |
| SHA256 | 76273382e4252c1f60a2251141e108942494409c759358320735891762c0682e | Blackwood.dll, custom Chisel tunneling wrapper |
| SHA256 | d3561bd4aad003dc3e08157b0891860bb496b80cd6e44901692e08ab1d4e8260 | Blackwood.dll.conf, contacting 91.107.156[.]29 |
| SHA256 | f5ba1645694c62f527ed6ceda8c68a5c3dd92b4032439167e8e937e72803b4bd | Blackwood archive, contacting 65.109.214[.]145 |
| SHA256 | 7cc571aca6d8715d9aaad3d83e1bcd30467565d583db1dfe73697c5d00a1f875 | Blackwood archive, contacting 87.248.129[.]239 |
| IP Address | 91.107.156[.]29 | Blackwood tunneling endpoint |
| IP Address | 87.248.129[.]239 | Infrastructure linked to Blackwood |
| IP Address | 65.109.214[.]145 | Credential-harvesting and Blackwood infrastructure |
| IP Address | 38.180.136[.]127 | Earlier phishing staging infrastructure |
| Domain | cloud.g-drive[.]cam | Phishing domain |
| Domain | googeldrive[.]cam | Phishing domain |
| Domain | drivegoogel[.]cam | Phishing domain |
| Domain | googelmeet[.]online | Phishing domain |
| Domain | meetonline[.]cam | Phishing domain |
| Domain | asdfafadafg[.]online | Phishing staging domain |
| Registry Key | HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run\MicrosoftRuntime | ShelbyLoader V2 persistence location |
| GitHub C2 | hxxps[:]//github[.]com/peakyblinders-tm | GitHub command-and-control infrastructure |
| GitHub C2 | hxxps[:]//github[.]com/GreenBeret0 | GitHub dead-drop resolution testing infrastructure |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC
